Solutions
GRC Software redefined: Integrated, automated, legally secure
Manage risks, controls, and compliance obligations without data silos. OPTURE is the GRC software for corporations and small and medium-sized businesses.
REAL SOFTWARE, NO ADHESIVE
Three departments. A common data base.
No more virtual dashboards. OPTURE GRC provides you with three fully-fledged, methodically independent software solutions (ERM, IKS and COM) on a central platform.
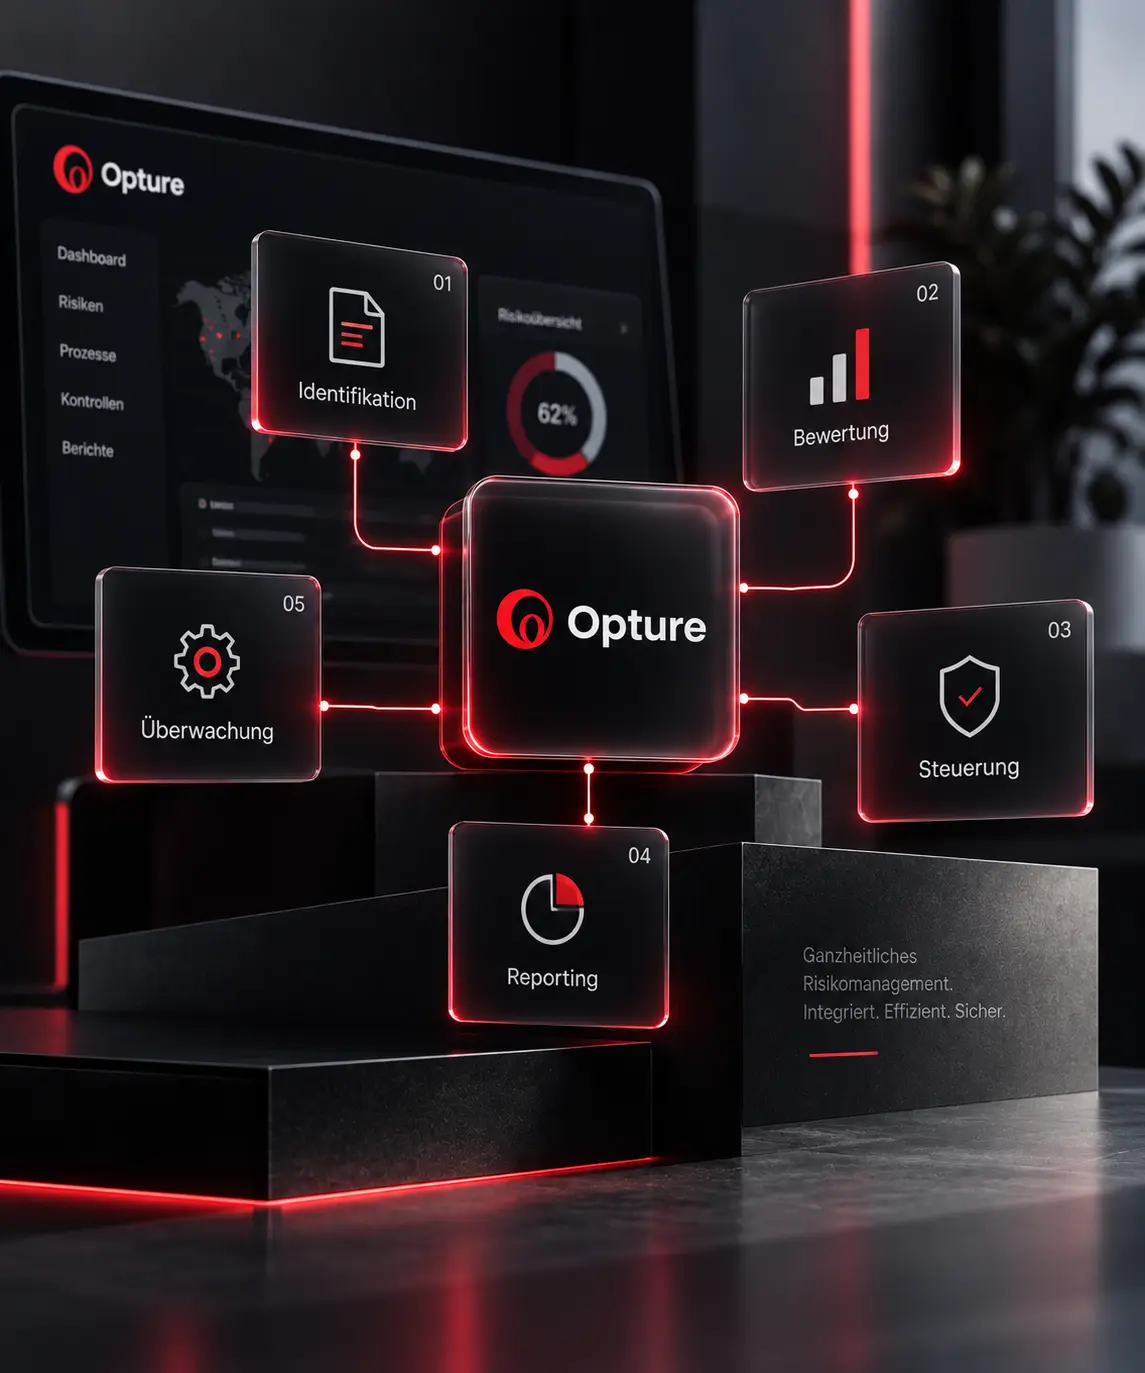
OPTURE ERM: Intelligent risk management
Form the whole Risk management-Process is cleanly managed from identification to reporting.
Quantitative models: Calculation of all relevant key performance indicators using powerful risk engines.
Automated workflows: System-driven ratings and approvals without manual follow-up.
Full transparency: Audit-proof documentation and real-time dashboards for management and oversight.
OPTURE IKS: Structured control systems
Link processes, risks and Checks in a clear, comprehensible model.
Automated execution: Control cycles and responsibilities are completely system-driven.
Immediate action: Weaknesses are automatically detected and corrective measures are initiated immediately.
Audited evidence: Every inspection carried out is fully documented and immediately verifiable.
OPTURE COM: Independent compliance
Regulatory Methodically correct control of obligations – completely independent yet deeply integrated into your GRC strategy.
Dynamic collection: Enterprise-wide Compliance-Status through intelligent questionnaires.
Independent evaluation: Compliance-Risks are recorded separately and intelligently handled ERM/IKS consolidated.
Audit Readiness: Complete evidence without lengthy manual proofing processes.
Customer Benefit
No more island solutions: Modern GRC management
Fragmented data and endless spreadsheets cost time and carry liability risks. OPTURE GRC connects all disciplines into a unified system.
Single Source of Truth
A unified data base for all GRC data. No redundancies, no media breaks, and no error-prone manual consolidation anymore.
Automated workflows
Reviews, controls, and approvals are carried out automatically across the system. Responsible parties are specifically notified, and deadlines are guaranteed to be met.
Real-time transparency
Risk-Heatmaps, Controlstatus and Compliance-Real-time fulfillment. The perfect and reliable basis for decision-making for management.
Everything you need to know about OPTURE GRC – explained in a nutshell
Our FAQ provide quick, understandable answers to the most important questions about the GRC topic.
How does OPTURE differ from other GRC suites?
Many competitors offer the topic as part of GRC. Compliance Only as a „view“ or aggregation. OPTURE GRC, on the other hand, provides three fully-fledged, independent modules. Furthermore, the software stands out for its mathematical depth and the complete automation of GRC processes.
Can we automate GRC processes?
Yes, absolutely. Risk reviews, control cycles, escalations, and reporting are all handled fully automatically. This reduces manual errors and drastically speeds up your governance processes.
How quickly can OPTURE GRC be implemented?
Thanks to our proven standard processes based on over 25 years of experience, companies are typically productive in the system after 4 to 6 weeks.
Is the system ready for future regulations?
How is the OPTURE GRC software integrated into the RegOS platform?
Deep Dive: The evolution of GRC software – From the island solution to the integrated control platform
In many companies, the areas of governance, enterprise risk management (ERM), and internal control systems (ICS) are historically treated in absolute silos. The result of this separation is fragmented data, redundant work processes, and an extremely high risk of compliance violations, as critical dependencies between departments are simply not recognized. A modern GRC software solution solves this problem through a centralized platform. However, caution is advised: the market is full of tools that promise more than they can technically deliver.
The architecture question: Deep integration vs. virtual aggregation
The biggest mistake in choosing a governance, risk & compliance system lies in underestimating the architecture. Classic GRC systems often only show compliance as a simplified aggregation of already existing ERM and IKS data. They sell a pure "list view" as a standalone module. This falls far short in a complex regulatory landscape.
OPTURE takes a fundamentally different approach here: Instead of aggregating data only virtually, the RegOS platform offers three independent, fully-functional modules. Risks, controls, and obligations are not only displayed but also linked systematically and actively managed. If the compliance module (COM) identifies a regulatory gap, an appropriate control can be planned immediately in the IKS and the resulting financial risk can be evaluated in the ERM. This eliminates information gaps and creates true, seamless governance.
System comparison: Classic GRC suites vs. OPTURE GRC
| Feature | Classical GRC systems | OPTURE GRC (RegOS) |
|---|---|---|
| Architecture | Modular segmentation, often inadequately linked. | Central platform with three fully-fledged, deeply integrated pillars. |
| Compliance approach | Often just a dashboard that reflects data from other areas. | Independent methodological representation of duties and proofs. |
| Risk assessment | Often purely qualitative checklists (red/yellow/green). | Professionally recognized models including quantitative Monte Carlo simulations. |
| Automation | Basic reminders via email. | Complete automation of risk reviews and escalation levels. |
Technological leadership: Modern models for complex requirements
In risk management, do not rely solely on simple checklists. A robust system requires methodical depth in every individual area. OPTURE GRC is based on professionally rigorously recognized, mathematically-founded models for risk and compliance.
Coupled with the highly-performant RegOS platform, this enables stable, lightning-fast and revision-safe processes – even in the most demanding enterprise environments with thousands of users. Through the massive reduction of manual effort, costs for reporting and audits are significantly lowered. Risks are transparent, opportunities are more quickly actionable.
From practice, for practice: Scalability for new regulations
Software must not be purely theoretical in nature. The OPTURE GRC solution reflects over 25 years of project experience in highly regulated industries. This is evident primarily in two aspects:
- Usability: The intuitive user interface ensures that even users (e.g., department managers) who rarely use the system for risk reporting can immediately navigate flawlessly and complete their tasks.
- Future security: The half-life of regulatory frameworks is drastically decreasing. Whether it’s the Supply Chain Due Diligence Act (LkSG), the Corporate Sustainability Reporting Directive (CSRD / ESG), the Whistleblower Protection Act (HinSchG), or IT security directives such as NIS2 – companies must react in an agile manner. Instead of acquiring an isolated software solution for each new law, the scalable architecture ensures that new regulatory modules can be seamlessly integrated into the existing OPTURE structure.