Solutions
State-of-the-art Privacy Management System (PMS)
The structured, audit-proof, and fully GDPR-compliant solution for your company. Manage all data privacy processes centrally in one place – and effortlessly meet the highest requirements from the GDPR, ISO standards, EU regulations, information security, and internal governance guidelines.
Benefits & Automation
Intelligent DSMS: Control data protection, reduce risks & ensure compliance
OPTURE DSMS seamlessly combines data protection management, risk assessment, action control, and documentation into a well-designed solution.
- Modern look and feel
- Intuitive usability
- Technologically leading
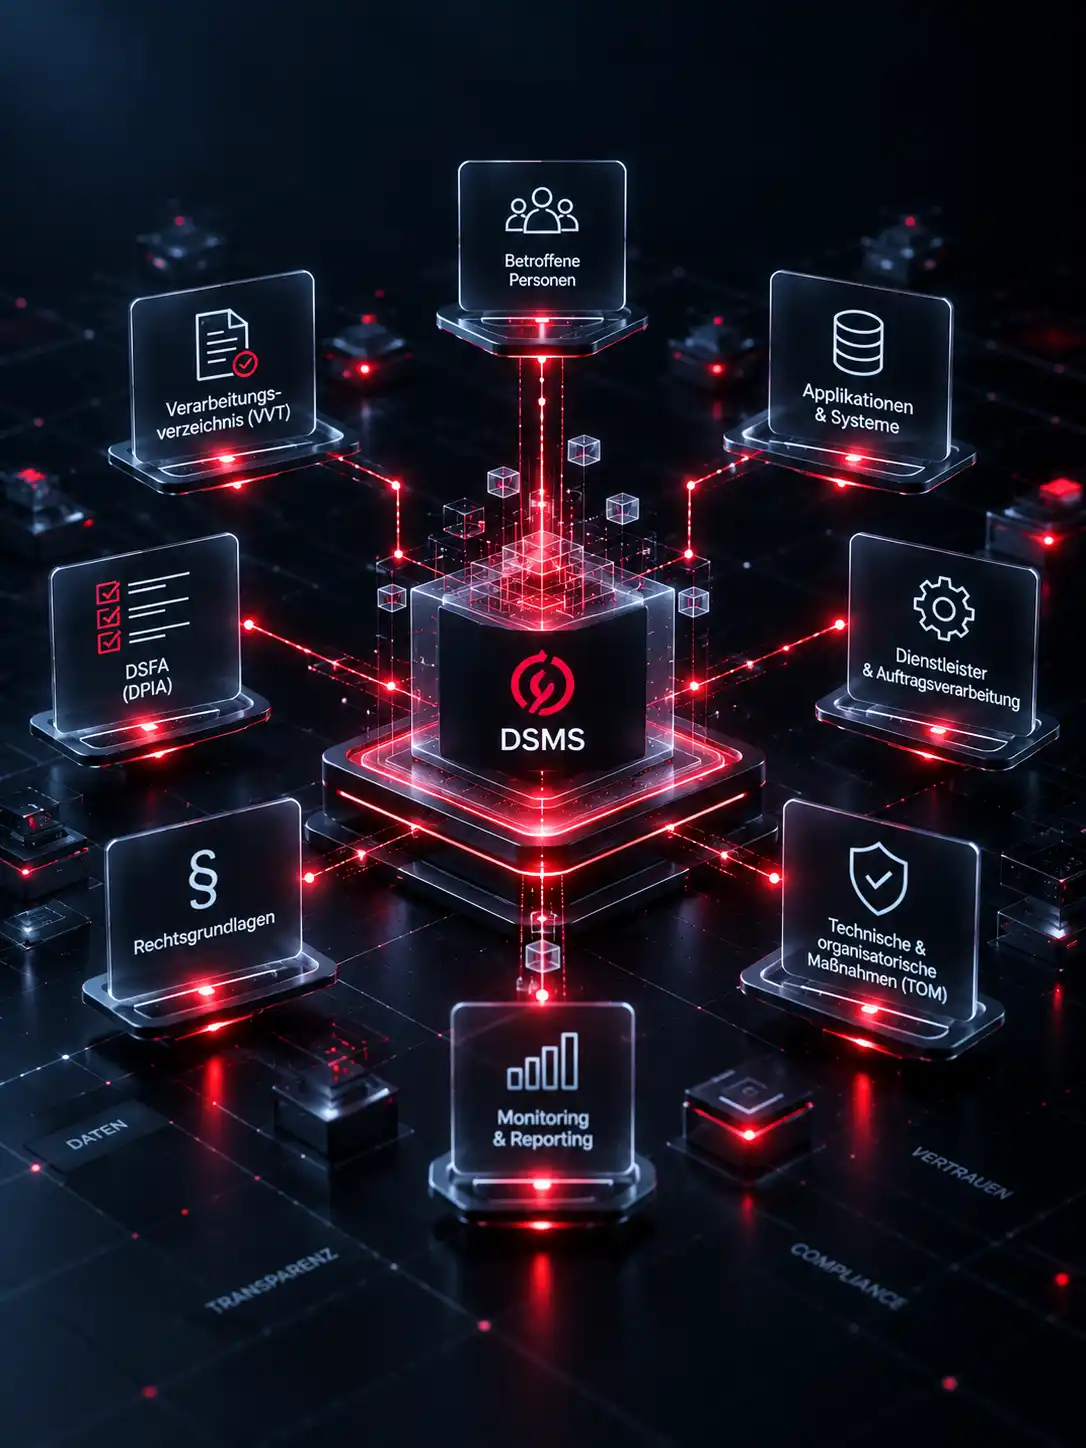
Dynamic Processing Directory
No longer record processing activities in isolation. The VVT in OPTURE DSMS is intelligently linked to applications, service providers, and legal bases. Departments can easily and directly submit their work using simple, guided forms within the system.
- VVT -> Process Description
- Legal basis, recipients & transfers
- Automated reporting
- Retention periods & deletion concept
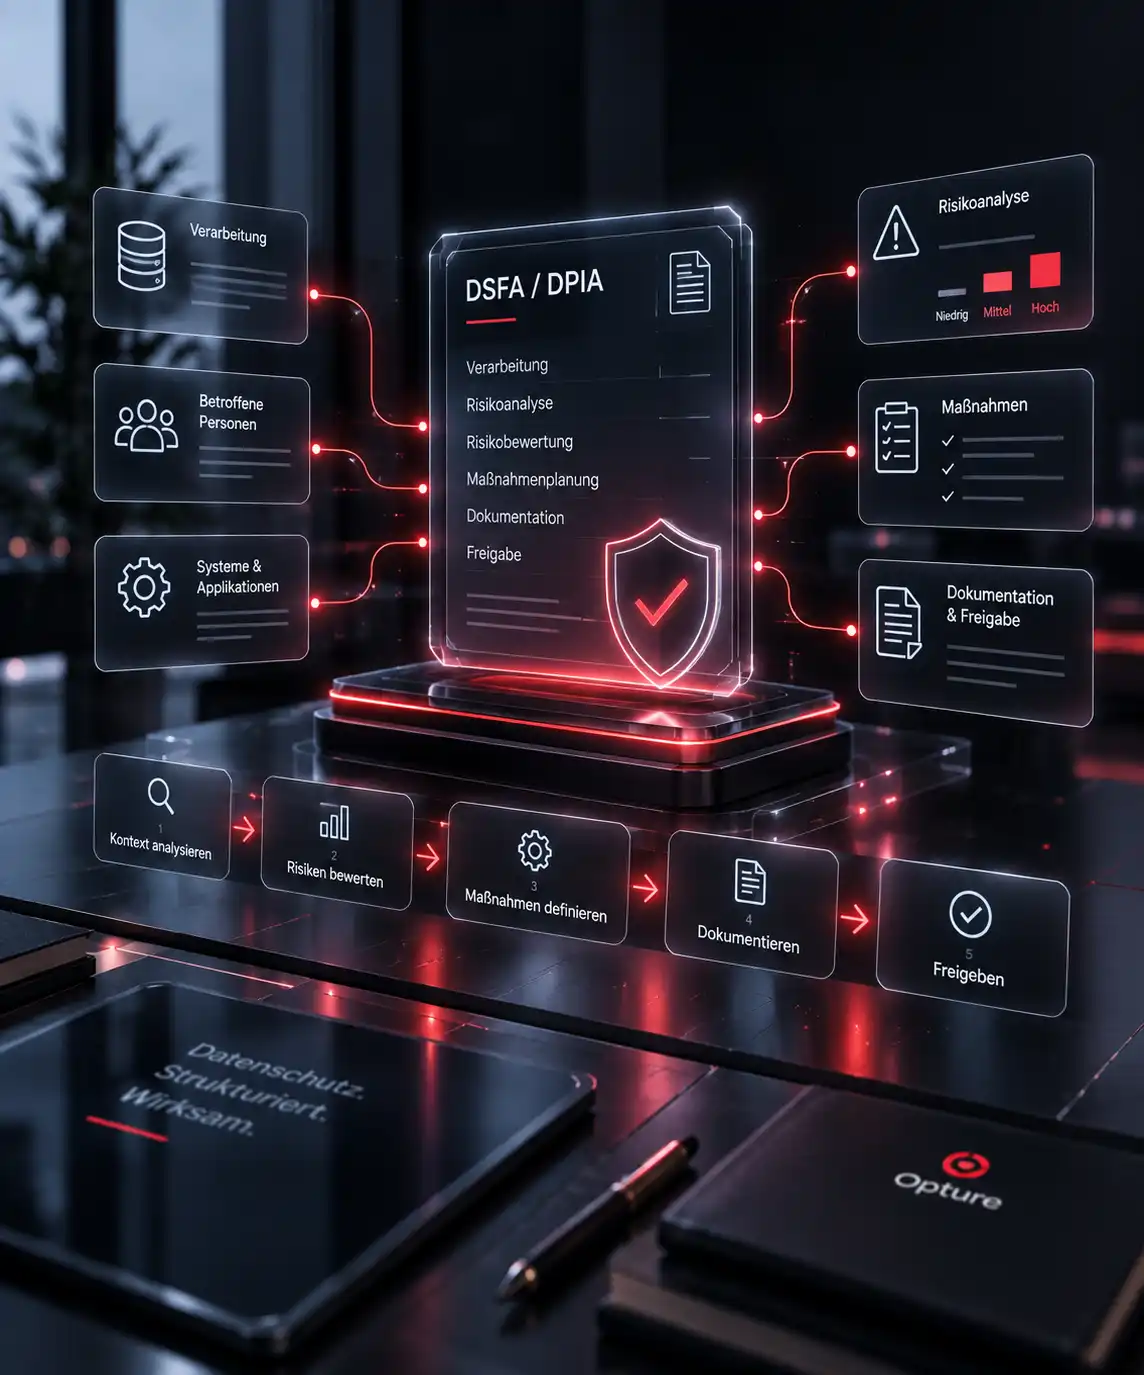
System-guided Data Protection Impact Assessment (DPIA)
If processing poses high risks to data subjects, the system guides you methodically through the threshold analysis and subsequent risk assessment, including action planning.
- Risk analysis
- Measures & Risk Reduction
- Documentation & Release
- Affected & Impact
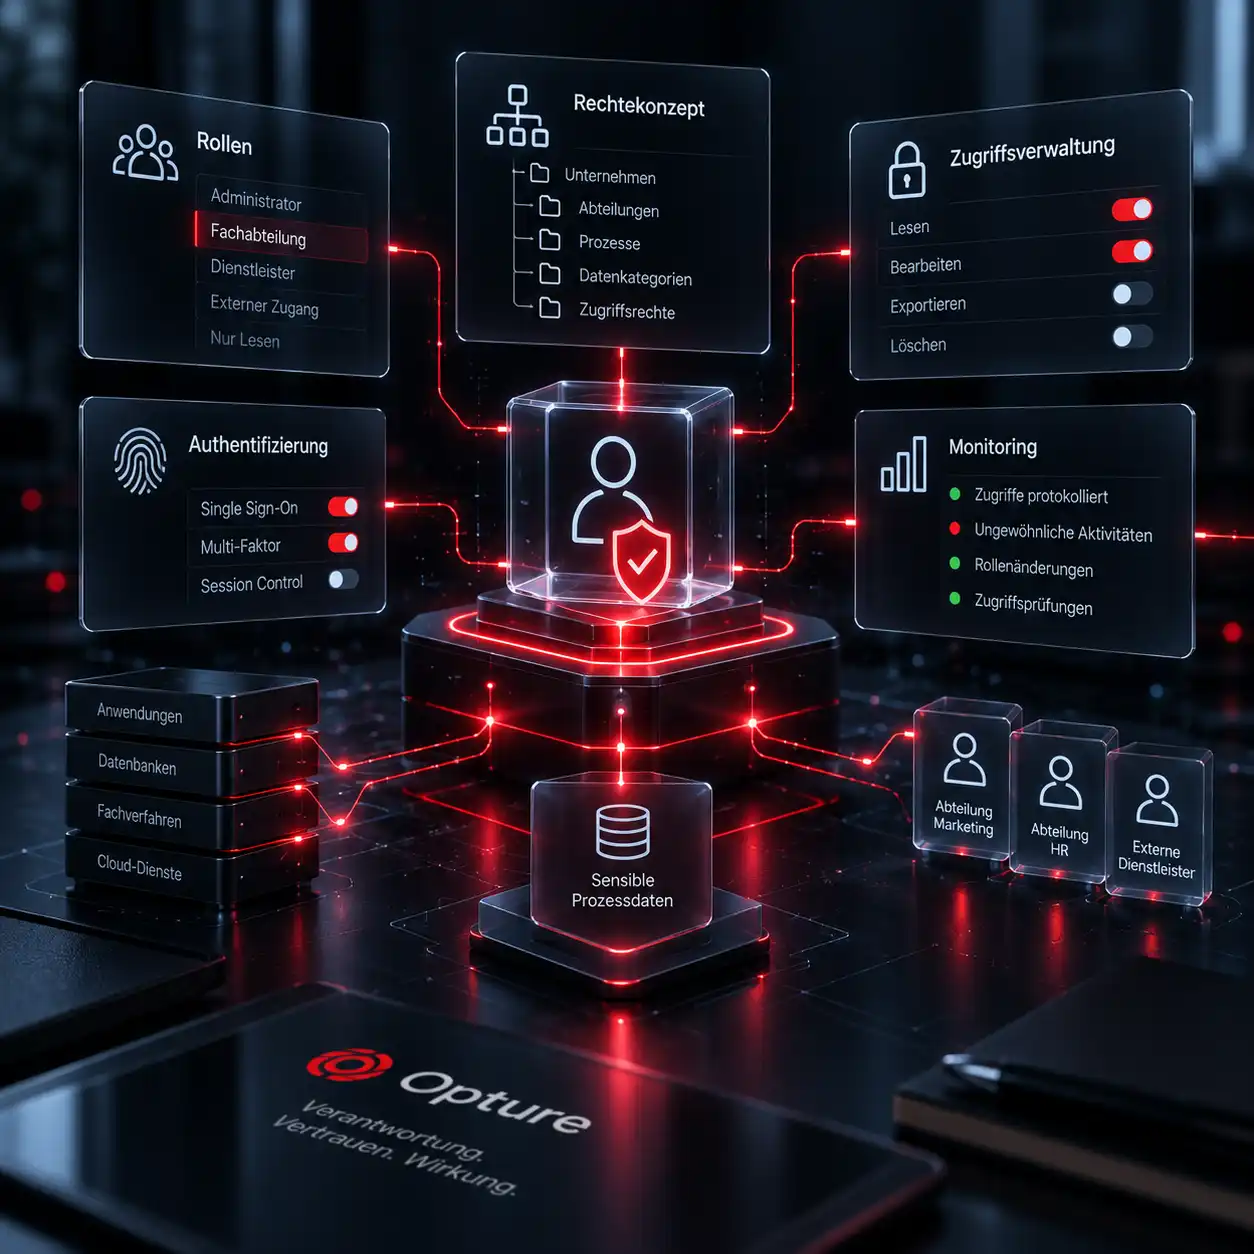
Granular, role-based access control
Paradoxically, DSMS tools are often themselves a privacy risk when everyone can see everything. OPTURE DSMS protects sensitive process data through a strict role-based system that precisely separates access based on departments or clients.
- Role and rights concept
- Access management
- Monitoring & Reviews
- Authentication & Security
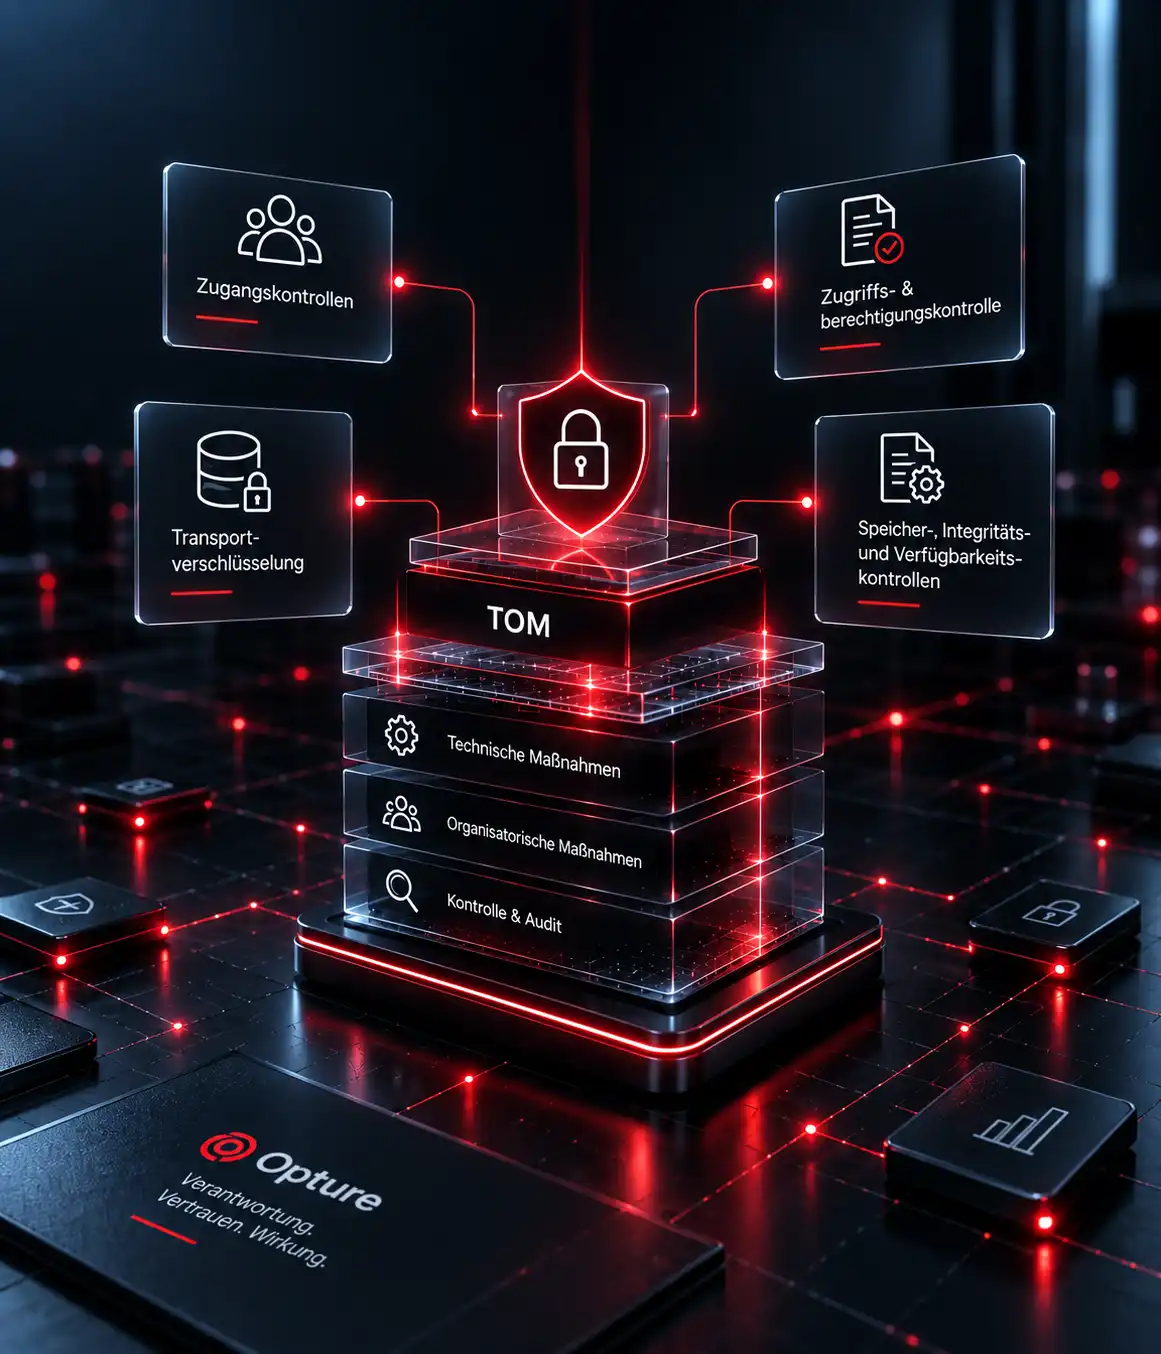
Technical and Organizational Measures (TOM)
TOMs represent the entire technical and organizational security architecture – without TOMs, no ISMS is auditable. TOMs are the security measures pursuant to Art. 32 GDPR that ensure personal data is processed in a protected, controlled, and auditable manner.,
- Access controls
- Access & Permission Control
- Transport encryption
- Storage, integrity and availability controls
Excel is out - OPTURE is in
How the innovative OPTURE DSMS works
Forget manual Excel lists and confusing email threads. The OPTURE Data Protection Management System combines a central platform with automated workflows, intelligent documentation, and seamless audit-proof security.
Centralized management of all obligations
Records of processing activities, TOMs, and data subject requests are bundled centrally in one place. Central management of all GDPR topics.
Automated Deadlines & GDPR Workflows
Data subject requests, DPIAs, and deletion processes follow standard procedures. Deadlines are monitored automatically.
Full transparency regarding risks
Make data flows and systems visible, identify vulnerabilities early, and minimize liability risks.
Audit readiness at the push of a button
Every action is immutably documented. Effortlessly meet the strict requirements of regulatory authorities and auditors.
OPTURE DSMS
Your competitive advantages with OPTURE DSMS:
An incident is not just a process or asset failure or a materialized risk. It is much rather a broken supply chain, a safety-related accident, a quality defect in production, or a violation of ESG– or GDPR guidelines. OPTURE ICM enables the structured, centralized recording of all these critical events. You receive a complete, unvarnished operational picture across all departments, locations, and subsidiaries.
Platform architecture instead of silo tools: Benefit from the combined power of the integrated OPTURE RegOS Platform for all governance processes.
Leading security architecture: Modern encryption and GDPR-compliant data processing – the perfect foundation for highly sensitive personal data.
Professional control: Say goodbye to error-prone Excel or email handling. Utilize real versioning and compliance management.
Absolute independence: Your data privacy is no longer dependent on individuals or vulnerable file servers. You have full control at all times.
Global Scalability: Designed for international organizations. Supports multi-entity structures, country-specific requirements, and multilingual environments.
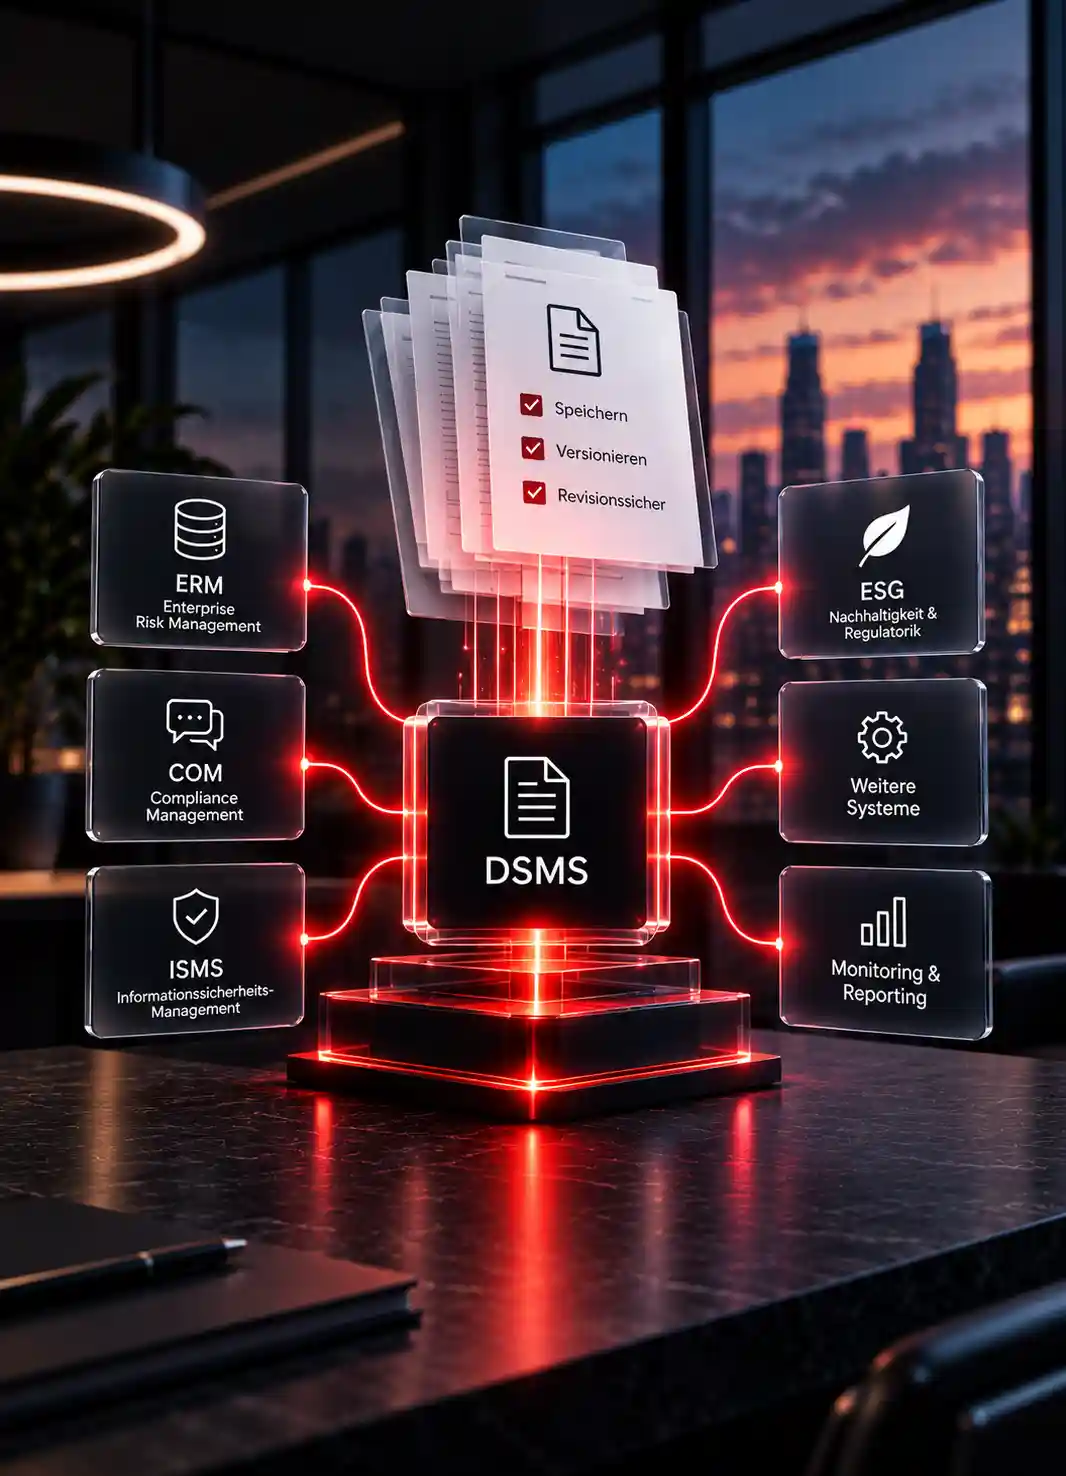
regulatory control model
Your competent partner: What makes OPTURE DSMS unique
Frequently asked questions about the topic of ISMS.
What specific benefits does OPTURE DSMS offer me?
The system strengthens your compliance, significantly reduces the manual effort required for data protection, and provides 100 % transparency regarding all processed personal data and internal processes.
How does the software support internal control?
Through predefined, structured workflows, clean versioning, comprehensive audit trails, and fully automated deadline monitoring.
How does OPTURE differ from other GRC tools?
OPTURE DSMS is more modern, more flexible to customize, and more secure. Thanks to its deep integration, it is the ideal solution for organizations with particularly high, complex data protection and security requirements. Compliance-Requirements.
How does access control work?
We use role-based permissions. You can control these with a high degree of granularity – entirely individually by document type, department, or specific security level.
How quickly can OPTURE DSMS be implemented at our company?
Very fast. Usually within 3 to 6 weeks. The system is completely customizable by you – without any lengthy IT projects or external service providers.
What is a Data Protection Management System (DPMS)? Definition & Meaning
In an increasingly data-driven economy, the protection of personal data is not only a legal necessity, but a crucial factor for trust and competitiveness. A Data Protection Management System (DPMS) is a systematic, holistic approach to the planning, implementation, monitoring, and continuous improvement of all data protection-relevant processes in a company. It serves to meet the requirements of the General Data Protection Regulation (GDPR) to structurally anchor in everyday business and to demonstrably fulfill accountability.
For management, data protection officers, compliance managers, and IT security, a modern DSMS means the transition from reactive damage control to proactive data protection management. An isolated Excel list of processing activities is no longer sufficient today. A professional DSMS interconnects processes, IT systems, service providers, risks, measures, and evidence in a central system.
The PDCA cycle in data protection
A functional data protection management is methodically based on the established PDCA cycle (Plan, Do, Check, Act), which is also used in ISO standards such as ISO/IEC 27701 for data protection or the ISO 27001 applies to information security. It ensures that data protection is not understood as a one-off project, but rather as an ongoing process.
The central idea: Data protection must be planned, implemented, regularly reviewed, and continuously improved. This is how a data protection management system is created that not only documents, but actively manages.
[Data Protection Objectives & Compliance Strategy]
               │
               ▼
    ┌───────────────────────┐
    │ 1. PLAN (Planning)     │
    │ Risk analysis, VVTs,  │
    │ Create guidelines │
    └───────────┬───────────┘
               │
               ▼
    ┌───────────────────────┐
    │   2. DO (Execution)   │
    │ Implement TOMs,  │
    │ Conduct training sessions│
    └───────────┬───────────┘
               │
               ▼
    ┌───────────────────────┐
    │  3. CHECK (Verification)   │
    │ Audits, controls,   │
    │ Incident monitoring   │
    └───────────┬───────────┘
               │
               ▼
    ┌───────────────────────┐
    │ 4. ACT (Optimization)  │
    │ Adapt processes,    │
    │ Address vulnerabilities│
    └───────────┬───────────┘
               │
               ▼
[Continuous Improvement Process]
1. Plan: Planning and design
In the planning phase, data protection goals, responsibilities, and relevant data flows are defined. This includes in particular the Record of Processing Activities (RoPA) pursuant to Art. 30 GDPR. Companies record which personal data is processed, for what purpose, on what legal basis, by which systems, and with which service providers.
2. Implementation and Execution
During the implementation phase, data protection measures are operationally anchored. These include technical and organizational measures (TOMs) in accordance with Art. 32 GDPR, role and permission concepts, encryption, access controls, employee training, and defined processes for data subject rights such as access, rectification, or erasure.
3. Check: Monitoring and Auditing
A DSMS must be reviewed regularly. Internal audits, control checks, data protection reviews, and monitoring processes show whether defined measures are effective. Data protection incidents, deadlines, reporting obligations, and deviations are also identified, evaluated, and documented in this phase.
4. Act: Correction and Optimization
If deviations, new risks, or vulnerabilities become apparent, measures must be adapted and processes improved. In the case of a high risk to the rights and freedoms of data subjects, a Data Protection Impact Assessment (DPIA) be required. In this way, data protection is continuously being further developed.
Core regulatory requirements and fine risks
The GDPR requires not only compliance with data protection regulations, but also proof of it. Companies must be able to demonstrate at any time which data is being processed, on what legal basis this takes place, which protective measures have been implemented, and how data subject rights, service providers, and data protection incidents are managed.
| GDPR Article | Requirement | Relevance for the DSMS |
|---|---|---|
| Article 5, paragraph 2 | Accountability | The controller must be able to demonstrate compliance with the data protection principles at all times. |
| Article 30 | Record of processing activities | The Records of Processing Activities (RoPA) form the central basis for transparency regarding data processing operations. |
| Article 32 | Security of processing | Technical and organizational measures must be defined, implemented, and documented. |
| Art. 35 | Data Protection Impact Assessment | High-risk processing activities must be systematically assessed and appropriate protective measures derived. |
| Article 28 | Data processing on behalf of a controller | External service providers must be managed contractually, organizationally, and verifiably. |
Real-world examples: Excel vs. modern DSMS software
Many companies still manage data protection processes in Excel lists, emails, and individual documents. In practice, this results in media discontinuities, unclear responsibilities, outdated documentation, and a high level of manual effort. Especially when handling data subject rights, data protection incidents, or audits, such structures quickly reach their limits.
Scenario: A data subject requests the deletion of their data
The manual method: The data protection officer has to search through various lists and systems to find out where the data of the data subject is stored. Afterwards, specialized departments are informed by email. Feedback, deadlines, and proofs must be checked manually.
With a modern DSMS: The software links processing activities, systems, controllers, and service providers together. Upon receipt of a request, an automated workflow starts. Department heads receive tasks, deadlines are monitored, and all processing steps are documented in an audit-proof manner.
The benefits of specialized DMS software
Modern data protection management must be dynamic, scalable, and audit-proof. Specialized DSMS software helps companies centrally control data protection processes, keep documentation up to date, and meet regulatory requirements in a permanently traceable manner.
- Central single source of truth: ROPAs, TOMs, contracts, consents, DPIAs, data protection incidents and evidence are centrally managed and version-controlled.
- Automated workflows and deadline monitoring: Tasks, reminders, escalations, and reviews relieve data protection officers and business departments.
- Risk-based data protection management: Processing activities, IT systems, service providers, and protective measures can be associated with risks and prioritized.
- Audit readiness at the push of a button: Evidence, reports, and processing histories are available in a structured format for audits or regulatory inquiries.
From data protection effort to integrated management tool
A professional DSMS does not reduce data protection to documentation and mandatory tasks. Through clear processes, automated workflows, and centralized evidence, data protection becomes a manageable component of governance, compliance, and information security.
Companies gain transparency into data processing activities, service providers, security measures, and risks. At the same time, manual effort decreases because reviews, deadlines, tasks, and documentation are systematically managed. This makes data protection audit-proof, efficient, and robust in the long term.